Defence & Technology

How defensive technology works — DLP, SIEM, SOAR, XDR and EDR — plus the anatomy of a ransomware attack. What each delivers and what it will not replace.

What is a SOC (Security Operations Center)?

Defence & Technology

What is a SOC (Security Operations Center)?

A SOC is a team that monitors an organisation's systems around the clock, assesses alerts and responds to incidents. We explain what it does day to day, who works in it, which tools it uses, how it differs from MDR and a SIEM, what Poland's KSC Act says about it and what to ask a provider.

11 min
What is XDR and how it differs from EDR

Defence & Technology

What is XDR and how it differs from EDR

XDR collects data from endpoints, identity, email, cloud and network, and links related events into one incident. We explain what it adds to EDR, how it differs from SIEM, what it does not do without people on duty, when to adopt it and what to ask a vendor.

15 min

What is SOAR? How it automates incident response

Defence & Technology

What is SOAR? How it automates incident response

SOAR is software that carries out defined steps once an alert exists: it gathers context, opens a ticket and triggers the response in other systems. We explain how a playbook works, how SOAR differs from SIEM, XDR and EDR, what to automate first and what to leave alone, and who needs it.

14 min

What is VDI and when do virtual desktops make sense?

Defence & Technology

What is VDI and when do virtual desktops make sense?

VDI means virtual desktops that run on the organisation's servers: staff connect from any device and the data stays in the data centre. We explain how VDI works, how it differs from remote desktop, RDP, DaaS and VPN, what it does for security, what it does not solve and when a rollout makes sense.

15 min

What is SIEM? How a SIEM system works and when you need one

Defence & Technology

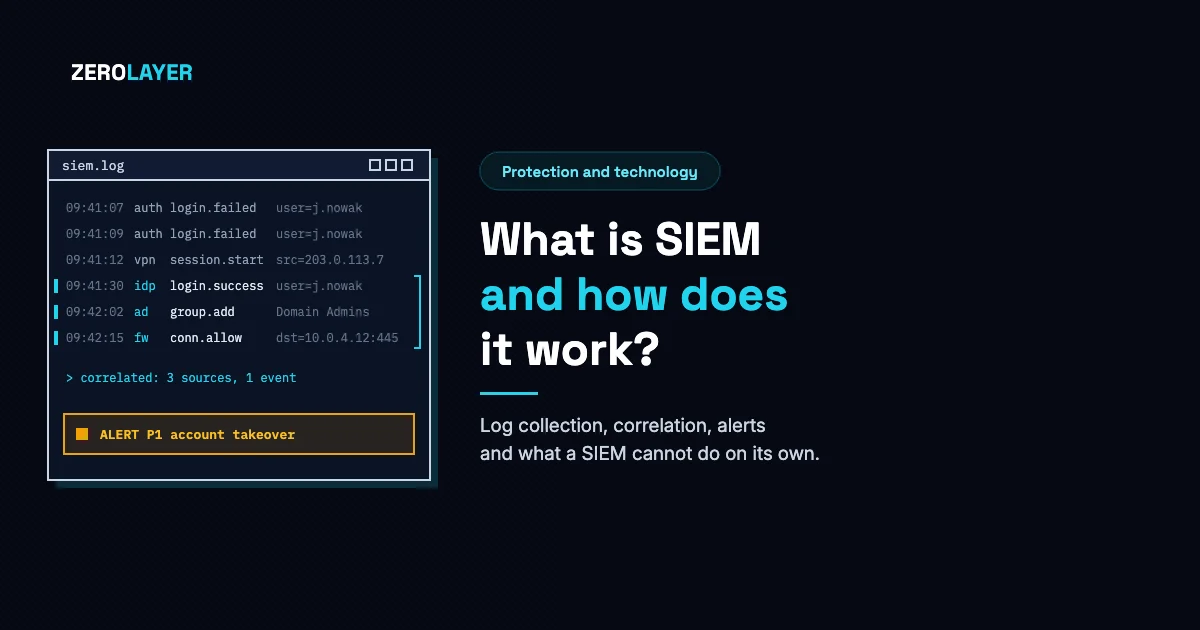
What is SIEM? How a SIEM system works and when you need one

A SIEM system collects logs from across the infrastructure, links them into events and raises alerts. We explain how it works in five stages, what it gives an organisation, which KSC Act and DORA obligations it helps meet, the problems to expect and where to start.

13 min

Penetration testing: what a pentest is, how it runs and how to choose a provider

Defence & Technology

Penetration testing: what a pentest is, how it runs and how to choose a provider

A pentest is a controlled attack carried out with written authorisation that checks whether security controls can be bypassed. We show how it differs from a vulnerability scan, how it runs in six stages, what the report should contain, which regulations require testing and what to ask a provider.

19 min

WAF (web application firewall): what it is, how it works and what it will not stop

Defence & Technology

WAF (web application firewall): what it is, how it works and what it will not stop

A WAF inspects every HTTP request before it reaches the application and blocks code injection, bots and attempts to exploit known vulnerabilities. We show how it differs from a network firewall, when it is required and why injection made up only 4% of vulnerabilities in CERT Polska audits.

15 min